A finance technology stack becomes difficult to govern when several applications can claim the same number, status or master record. The problem is rarely the number of tools by itself. It is the absence of an agreed answer to three questions: which system may create or change a record, when authority moves to another system, and what evidence proves the handoff completed.
This reference architecture treats ERP, planning, billing, treasury, consolidation, reporting and finance data as distinct layers with explicit boundaries. It is designed for target-state decisions, not product selection or interface design.
Quick answer
A finance stack is defensible only when each governed object has one authoritative owner and every cross-system handoff has an explicit control and exception path.
Decision: Define the target application layers, authoritative systems and ownership boundaries across ERP, planning, billing, treasury, reporting and finance data.
Key takeaways
- Assign authority by finance object and lifecycle status, not by broad application label.
- Keep posted accounting actuals in the ledger, approved plans in the planning layer, billing events in billing, bank reconciliation in cash management, group adjustments in consolidation and derived measures in the analytical layer.
- Every cross-system handoff needs a control total, posting or acknowledgement status, reconciliation rule and named exception owner.
- A suite and a specialist application can both fit the architecture when their write rights and evidence boundaries are unambiguous.
Finance technology stack reference architecture at a glance
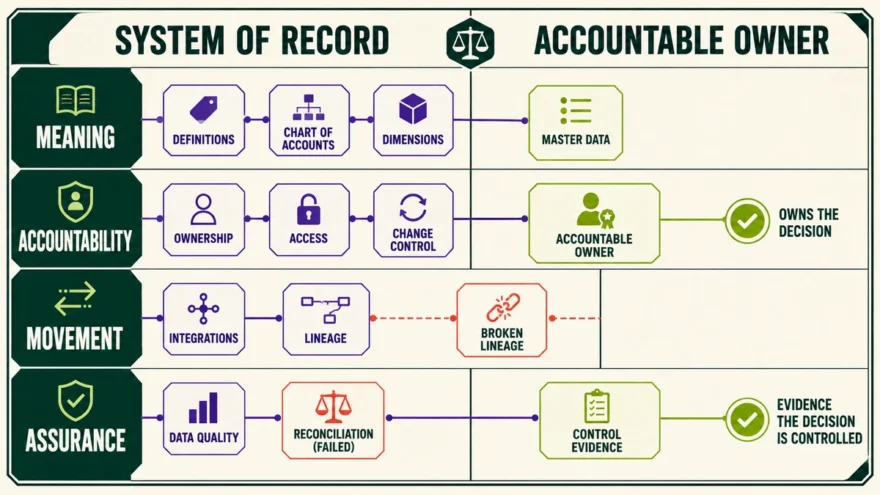
For this guide, a system of record is the application or external record authorized to create, amend or confirm a governed object at a defined lifecycle status. That definition is narrower than calling one platform the source for all finance data. An invoice, for example, can begin as a calculation in billing, become an open receivable in a subledger, produce a posted journal in the general ledger and later appear as a derived measure in a reporting model. Authority changes by status, while the record lineage remains connected.
| Layer | What it should authoritatively own | What it should not silently replace |
|---|---|---|
| Operational and commercial sources | Approved customer, contract, workforce, procurement, usage and fulfilment facts before they become finance records | Posted accounting, approved forecasts or consolidated results |
| Billing and receivables operations | Charge calculation, invoice preparation and lifecycle status; receivable detail after accounting creation | General-ledger actuals or bank-side settlement evidence |
| ERP and accounting | Legal-entity books, subledger accounting, journal entries, accounting dimensions and posted actuals | Planning assumptions, bank statements or management-only metric definitions |
| Planning and performance | Approved budgets, forecasts, scenarios, targets, assumptions and management plan versions | Correction of posted actuals or transaction-level operational records |
| Treasury and banking | Internal cash position, bank-account administration, payment workflow, acknowledgements and bank reconciliation | The bank’s external statement or the ledger’s accounting classification |
| Consolidation and controlled reporting | Group translation, eliminations, consolidation adjustments, consolidation status and controlled group outputs | Source legal-entity transactions |
| Finance data and analytics | Governed historical copies, conformed dimensions, semantic measures, analytical models and dashboards | Transaction correction, accounting approval or plan approval |
| Cross-cutting control plane | Identity, write access, master-data governance, interface monitoring, reconciliations, exception queues and change evidence | Business ownership of the underlying finance object |
The map is a logical model. A single suite may contain several layers, and one specialist platform may perform more than one role. The architecture decision is still made at the object and status level. Product boundaries do not remove the need to state who can write, approve, reconcile and correct each record.
The governing rule: one authoritative owner per object and status
Two systems may hold the same identifier or amount, but they should not both have unrestricted authority over the same object in the same status. The test is not whether data is duplicated. Reporting, planning and operational workflows often require copies. The test is whether a user or automated process can change the governed value in more than one place without a defined precedence rule.
Invoice status illustrates the point. Stripe’s invoicing documentation distinguishes draft, open, paid, void and uncollectible states, with different permitted actions at each stage. A finance architecture should make the same distinction even when another billing platform is used. Billing may own the editable draft and finalization event. The receivables subledger may own the open item and accounting status. Cash management may own matching to a bank statement. The general ledger owns the posted accounting effect. A dashboard can display all four, but it should not become an alternate place to repair any of them.
This status-specific model prevents a common design error: declaring the ERP, data warehouse or planning platform the single authority for every fact. The better rule is one authoritative owner for each governed object at each lifecycle state, with traceable handoffs when authority changes.
The finance systems integration map applies those authority boundaries at interface level, including contracts, retries, monitoring and reconciliation.
How to bound each finance system layer
ERP and accounting: own the books and posted actuals
The accounting layer should own the legal-entity ledger, accounting calendar, chart of accounts, subledger accounting and posted journals. SAP describes its Universal Journal as the book of original entry for Financial Accounting and Controlling transactions. The product-specific implementation will vary, but the architectural boundary is useful: once a transaction is posted as an accounting actual, corrections should follow the ledger’s controlled adjustment or reversal process.
Planning systems, billing systems and analytical models can receive accounting actuals. They should not overwrite them locally and present the altered value as booked actual. When a downstream user finds an error, the exception should return to the accounting owner, be corrected in the authorized layer and then flow forward again.
Planning and performance: own approved plan versions and assumptions
The planning layer should own budgets, forecasts, scenarios, targets, planning assumptions and their approval state. Oracle’s planning documentation separates scenario from version: a scenario identifies a data type such as budget, actual or forecast and its time span, while versions represent outcomes or iterations such as draft and final.
That distinction should appear in the target architecture. FP&A needs authority over forecast methods, scenario assumptions and approved versions. It does not need authority to edit imported ledger actuals. Actuals should arrive with period, entity, account, currency and load-status controls, then remain identifiable as accounting-derived data.
Billing and receivables: separate commercial calculation from accounting
Billing should own pricing inputs, usage or quantity inputs received from operational sources, invoice calculation, tax inputs where applicable, invoice finalization and customer-facing invoice status. The receivables subledger should own the open item, applications, adjustments, credit balances and accounting status after the invoice is accounted.
The boundary matters because billing status and accounting status are related but not identical. Oracle identifies its Receivables to General Ledger Reconciliation Report as the primary tool for reconciling receivables data to the general ledger. That need for reconciliation is evidence that the subledger and ledger perform distinct jobs even when they are modules in one suite.
A controlled handoff should preserve invoice ID, customer or account ID, legal entity, currency, accounting date, line totals, tax and total amount. It should also record rejected items and the owner responsible for resolving them.
Treasury and banking: distinguish internal position from external bank evidence
Treasury or cash-management software should own the internal cash position, account coverage, payment workflow, liquidity classifications and reconciliation status. The bank statement remains the external evidence of bank-side transactions and balances. The ledger remains the authority for the accounting treatment.
Oracle’s cash-management documentation describes reconciliation as selecting bank-statement lines and system transactions to be matched, including one-to-one and grouped matches. The architecture should therefore retain both sides of the match, the rule or user action that linked them, and a queue for unmatched or ambiguous items.
Payment initiation needs the same clarity. One designated system should create or release the instruction for each payment channel. Approvals may originate elsewhere, but the final release right, bank acknowledgement, rejection status and resubmission path must be assigned rather than inferred.
Consolidation and reporting: own the group result, not source transactions
The consolidation layer should own entity hierarchies used for group reporting, currency translation, intercompany eliminations, ownership calculations, consolidation journals and the status of the group result. Oracle defines consolidation as gathering data from descendant entities and aggregating it to parent entities, with translation where child and parent currencies differ.
Local books should remain intact. Group-only eliminations or adjustments belong in the consolidation layer unless accounting policy requires a legal-entity posting. Controlled reporting can then publish statutory and management outputs from the approved consolidation state, with version, period, entity scope and sign-off preserved.
Finance data and analytics: own the analytical representation
A warehouse, lakehouse or semantic model should own historical analytical copies, conformed dimensions, transformation logic and governed metric definitions. Microsoft recommends a data warehouse and extract, transform and load processes for demanding scenarios, with the semantic model connecting to the warehouse. That is an analytical architecture, not permission to repair source transactions in the reporting layer.
Finance data teams should be able to correct mapping logic, dimensional history and metric definitions through controlled changes. They should send transaction or accounting errors back to the authoritative operational or ledger owner. Each published measure should state its source, grain, currency treatment, period logic and reconciliation point.
The cross-cutting control plane: make the boundaries operable
System boundaries have little value unless access, monitoring and evidence support them. The 2025 GAO Green Book, which applies to US federal agencies, emphasizes documented risk assessment, preventive control activities and internal-control responsibility at multiple management levels. It is useful here as a control-design lens, not as a private-sector requirement.
For each layer, the control plane should define write access, approval authority, master-data change rights, interface monitoring, control totals, reconciliation frequency, evidence retention and exception escalation. Technology operations may run the platform, but the finance owner remains accountable for the governed object and its control outcome.
System-of-record, ownership and boundary matrix
The matrix below is a starting model. Replace generic application labels with the actual platform and named owner in the target architecture. Where one suite contains several modules, keep the rows separate so that write rights, statuses and controls remain explicit.
| Finance object or decision | Authoritative system or evidence | Business owner | Boundary rule | Minimum handoff or control evidence |
|---|---|---|---|---|
| Legal entity, chart of accounts and accounting dimensions | ERP master-data service or governed finance master-data platform | Controller with finance-systems owner | Downstream systems consume approved values and do not create competing local codes | Approved change record, effective date, replication result and rejected-record queue |
| Customer and contract terms used for billing | CRM or contract-management system until approved for billing | Commercial operations with legal or policy owner | Billing consumes the approved version and records the version or effective date used | Contract ID, customer ID, approval state, effective dates and completeness check |
| Usage, quantity or fulfilment event | Operational source that produced the event | Product, service or operations owner | Billing calculates from accepted events and does not reconstruct missing source activity without an approved rule | Source period, event count, rejected-event count and total quantity |
| Draft invoice and charge calculation | Billing platform | Billing operations | Editable while draft; calculation changes follow controlled pricing and approval rules | Calculation trace, price or rate version, tax input, approver and invoice total |
| Finalized customer invoice and billing status | Billing platform | Billing operations with AR | Finalization creates a stable invoice record; later changes use an allowed adjustment, credit or replacement path | Invoice ID, finalization timestamp, currency, line total, tax, total and delivery status |
| Receivable open item and application status | AR subledger in ERP or accounting platform | AR or credit control | Billing status does not replace the accounting open-item record | Accounting batch ID, accepted and rejected counts, control total and subledger-to-ledger reconciliation |
| Journal entry and posted actual | General ledger | Controller | Downstream systems may report the posting but cannot alter the booked value | Journal ID, balanced debit and credit, source, period, posting status and approver where required |
| Budget, forecast, scenario and target | Planning platform | FP&A with accountable business owners | Planning owns assumptions and approved versions; imported actuals remain accounting-derived | Scenario, version, period, assumption set, approval state and actuals-load status |
| Bank statement line and bank-reported balance | Bank statement or direct bank data as external evidence | Treasury | Internal systems retain the received record and do not rewrite bank evidence | Bank account, statement ID, sequence or timestamp, opening and closing balances and import status |
| Internal cash position and reconciliation status | Treasury or cash-management platform | Treasury | Position is derived from covered accounts and transactions; ledger and bank differences remain visible | As-of time, account coverage, source freshness, unreconciled items and book-to-bank difference |
| Payment instruction and release status | Designated ERP payment module, treasury platform or payment hub | Treasury or AP, according to payment policy | Only one system releases a given instruction; bank acknowledgements and rejections return to that record | Instruction ID, approval chain, release timestamp, acknowledgement, rejection reason and resubmission link |
| Consolidated group result | Consolidation platform | Group controller | Translation, eliminations and group adjustments do not alter legal-entity source books | Entity scope, period, source-load totals, translation status, elimination status, consolidation status and sign-off |
| Published management metric | Governed semantic or reporting model | CFO delegate, FP&A and finance-data owner | The layer owns the definition and presentation, while source errors are corrected upstream | Metric definition, model version, grain, currency and period rules, source lineage and reconciliation |
| Historical analytical dataset | Finance data warehouse or lakehouse | Finance data owner | History and transformations are controlled; the dataset is not an alternate transaction-entry system | Load ID, source extracts, row counts, control totals, transformation version and data-quality exceptions |
Six boundary tests before approving the target architecture
- Authority test: Name the one system allowed to create, change, cancel or approve the object at each status. If two systems can perform the same write without precedence, the boundary fails.
- Lifecycle test: State the event that transfers authority, such as invoice finalization, accounting posting, bank acknowledgement, plan approval or consolidation sign-off. Record the identifiers that connect the before and after states.
- Posting and reconciliation test: Define the control total, record count, amount, currency, period and acceptance status used to prove the handoff. State how subledger-to-ledger, book-to-bank and source-to-report differences are investigated.
- Master-data and access test: Assign who may change entity, account, customer, supplier, bank-account and reporting dimensions. Confirm that downstream copies cannot bypass the approved change route.
- Grain and timing test: Specify transaction grain, aggregation, effective date, accounting date, as-of time and refresh expectation. A real-time dashboard built on daily accounting extracts is still daily for that measure.
- Exception and evidence test: Name the owner, queue, service expectation, escalation and retained evidence for rejected, missing, duplicate, late or ambiguous records. An automated handoff without an owned exception path is incomplete.
Suite versus specialist systems is a boundary decision
A suite can reduce the number of handoffs and place ledger, subledger, master data and reporting controls under one administration model. That is valuable when shared accounting dimensions, legal-entity consistency and close control matter more than specialized process depth.
A specialist system can be justified when billing logic, treasury connectivity, planning methods, transaction volume or user workflow exceeds what the suite can support. The specialist should not be approved on functional depth alone. It also needs stable identifiers, explicit write rights, complete status returns, reconciliation evidence, security ownership and an exit path for failed transfers. For AI-supported bank workflows, the Moody’s AI systemic dependency warning adds a second boundary test: prove that model and cloud dependencies are mapped, substitutable and covered by a funded exit plan.
| Choice | Use when | Do not approve when |
|---|---|---|
| Suite-led | Common master data, accounting control and fewer handoffs outweigh specialist depth | Modules still create duplicate authorities or force uncontrolled offline work |
| Specialist-led for one domain | A distinct calculation, connectivity or workflow need has a named owner and controlled interface | The system can write accounting, payment or reporting states without clear precedence and reconciliation |
| Mixed architecture | Different layers have genuinely different jobs and the operating model can govern the handoffs | No team owns cross-system failures, master data or end-to-end evidence |
Turn the reference architecture into an operating register
- Inventory governed objects and statuses. Begin with the objects that affect financial statements, cash, plans and management reporting. Avoid starting with a product list.
- Assign the authoritative application and accountable owner. Record the system, finance owner, technology owner, legal entity or business scope and allowed write actions.
- Document every transfer of authority. Capture the triggering event, identifiers, timing, grain, control totals, acknowledgement and required reconciliation.
- Attach the exception operating model. Name the queue, resolver, escalation, ageing rule and evidence retained for each failed or disputed handoff.
- Govern architecture changes as control changes. Reassess the register when a new application, entity, bank, billing model, reporting requirement or data transformation changes an authoritative record or handoff.
The completed register should be usable by finance, technology, data and control owners in the same review. It should show not only where data resides, but who may change it, what event moves it, how the transfer is proven and where an exception is resolved.
Frequently asked questions
Can a data warehouse be the source of truth for finance transactions?
An analytical warehouse or semantic model can own the governed representation used for analysis without becoming the authority for source transactions. Posted entries, invoices, bank evidence and other operational records should retain their designated system owners. The architecture should document transformation, lineage and reconciliation so an analytical copy cannot silently acquire write authority.
How should finance choose between a suite and specialist systems?
The suite-versus-specialist decision should follow object ownership, lifecycle boundaries and the organisation’s ability to govern handoffs, not a product count. A suite can reduce transfers, while specialist systems may fit distinct jobs; either model fails when no team owns cross-system evidence, master data, exceptions or changes to authoritative records.
What should a cross-system handoff register record?
A cross-system handoff register should identify the governed object, authoritative application, finance and technology owners, triggering event, identifiers, timing, grain, control totals, acknowledgement and reconciliation. It should also name the exception queue, resolver, escalation, ageing rule and retained evidence so each transfer of authority can be operated and reviewed.